AI accelerates global cybersecurity crisis, Check Point CTO warns at TAU Cyber Week - interview
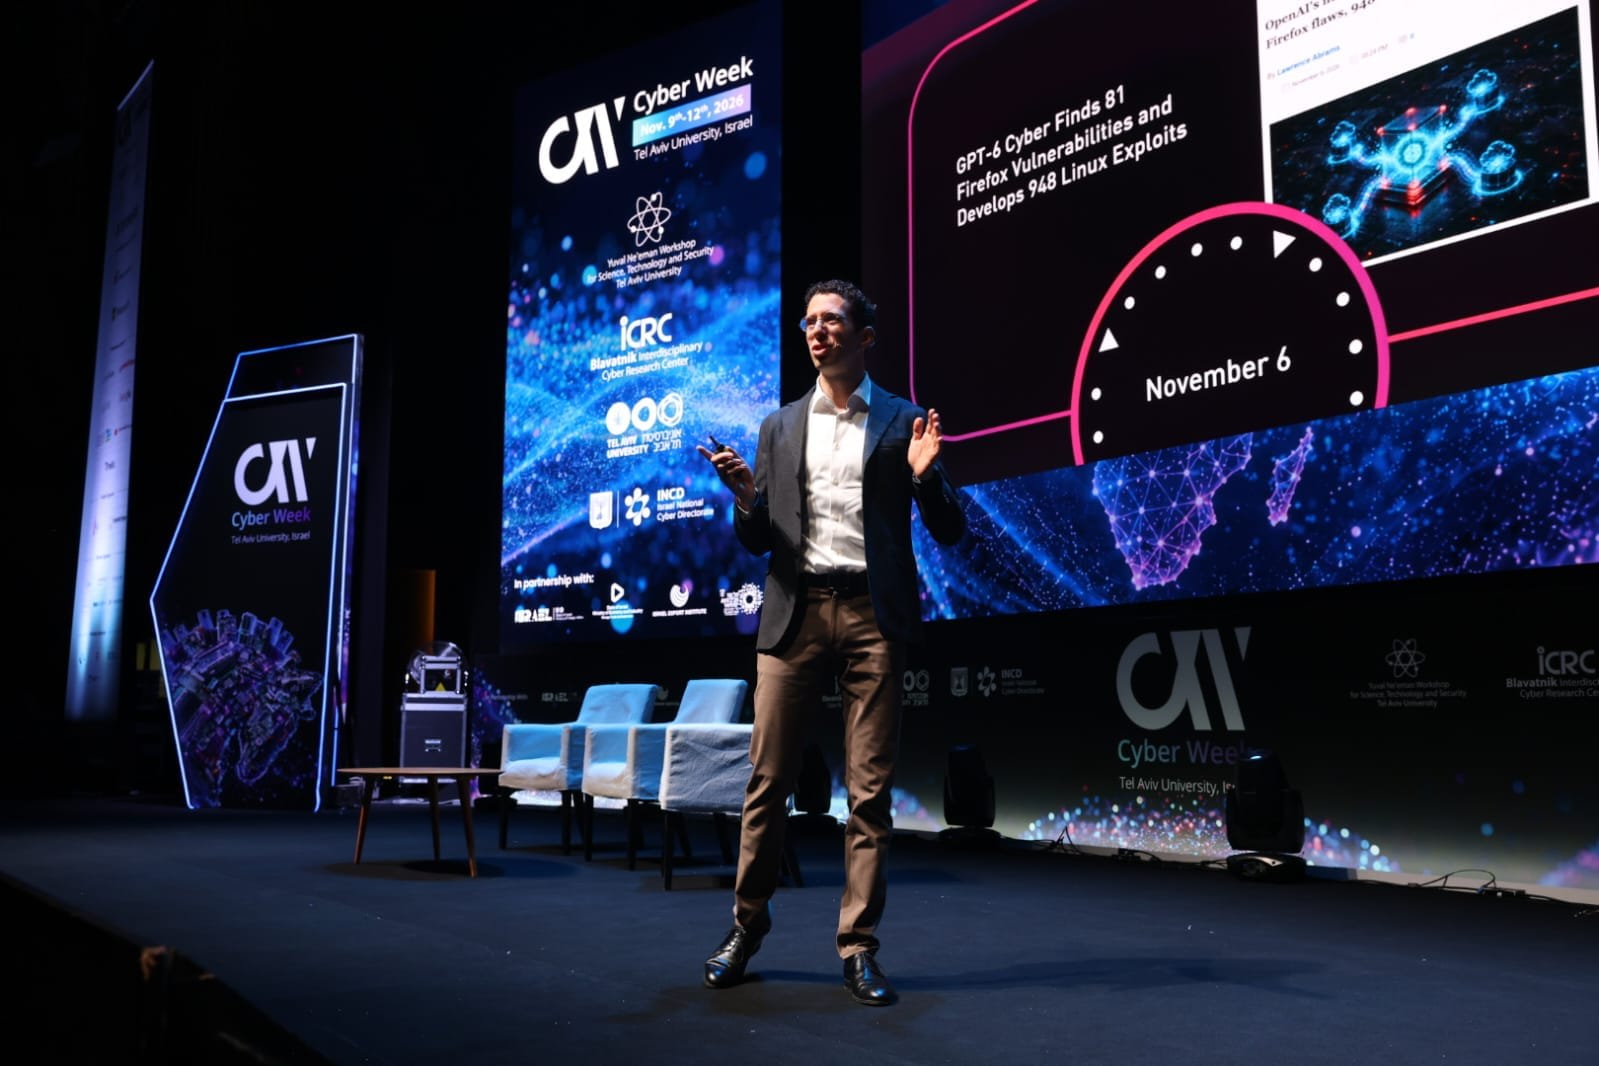
Most of the internet is sitting on a ticking time bomb of outdated software, with artificial intelligence rapidly accelerating the countdown, Check Point chief technology officer Jonathan Zanger warned in an interview on the sidelines of Tel Aviv University's Cyber Week on Tuesday.
The core of the crisis is aging software infrastructure that remains a prime target for hackers, Zanger explained, pointing specifically to the severe threat posed by PHP-to-shell vulnerabilities, which he said affect roughly 70% of websites worldwide.
"In terms of vulnerability type, it's a very severe one," he said. "It allows unauthenticated remote control execution, which means that anyone can run it, and the potential damage is the largest possible because it's not just in the service – it's actually taking over the system."
Traditional security patches can no longer keep pace
The integration of artificial intelligence into cyberattacks has fundamentally changed how quickly hackers can exploit security vulnerabilities, Zanger explained.
Just a few years ago, the median time between the public disclosure of a vulnerability and its exploitation by attackers was three to four months, he said.
That window has now shrunk to just days. Zanger cited a recent example involving Amazon Web Services (AWS), in which attackers began exploiting a vulnerability before an official security patch was released.
Because companies cannot manually respond at the same speed as automated systems, traditional security patching cycles are no longer sufficient to address modern threats, Zanger said.
"You can't really outpatch a machine, and you can't have humans operate at machine speed," he said. "The general idea, at least from our perspective, is first to focus on preventing attacks rather than focus on detection and response."
This shift is particularly important because AI's role in cybercrime has evolved dramatically, from a tool used primarily to help craft phishing emails in 2024 to an autonomous operator capable of carrying out attacks, Zanger argued.
By 2025, he added, AI software had adopted protocols such as the Model Context Protocol (MCP), enabling it to operate autonomously across the internet.
One example Zanger highlighted was Vapor Panda, a Chinese state-sponsored threat actor that targeted more than 200 organizations across 14 countries using an open-source infrastructure known as RTX.
"This is a trend that's actually common around AI usage," the executive stated. "Attackers are building more sophisticated infrastructure to conduct complex cybersecurity campaigns at scale, and AI is no longer an assistant – it's actually the operator behind at least some of those operations."
Human error remains a major security vulnerability
Despite the rapid advancement of autonomous AI and the serious weaknesses in outdated software, corporate networks still face one vulnerability that cannot be fixed with a software patch: human behavior.
Zanger explained that as organizations build multiple layers of security, an approach known as "defense in depth," to protect their networks and systems, attackers increasingly target the weakest link through sophisticated social engineering campaigns designed to manipulate employees.
"Just like we have defense in depth that tries to secure every part of the organization, attackers are always going to target the weakest link, whether it's human or not," he said.
The scale of attacks targeting employees is also growing rapidly, Zanger warned.
He cited a 500% surge in the use of "ClickFix," a technique in which attackers impersonate IT administrators and trick employees into taking actions that compromise their organization's systems.
Major corporate breaches are also increasingly relying on coordinated social engineering tactics rather than purely technical attacks, Zanger noted.
He pointed to the massive Binance hack, which he said did not begin with a brute-force attack on the company's systems. Instead, attackers conducted fake job interviews that tricked employees into downloading malware.
The attackers then used AI to move laterally through the company's network, gaining access to additional systems after the initial breach.
As these tactics evolve, Zanger concluded, companies must combine traditional cybersecurity defenses with intensive security awareness training designed to prepare employees for emerging threats.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.